GOVERNANCE BY DESIGN

GOVERNANCE BY DESIGN

GOVERNANCE BY DESIGN

Govern your AI solutions, not just the tools they’re built on.

Govern your AI solutions, not just the tools they’re built on.

Govern your AI solutions, not just the tools they’re built on.

RiskAlmanac captures each solution as a blueprint of how it actually works, then puts the right guardrails in place for the stage it’s in, from ideation to production. Days, not weeks, and defensible to anyone who asks.

RiskAlmanac captures each solution as a blueprint of how it actually works, then puts the right guardrails in place for the stage it’s in, from ideation to production. Days, not weeks, and defensible to anyone who asks.

Now taking a small number of design partners.

Now taking a small number of design partners.

Now taking a small number of design partners.

One blueprint producing risks, severity, controls and evidence

8

8

COMPONENTS MAPPED

COMPONENTS MAPPED

7

7

INTERACTIONS MAPPED

INTERACTIONS MAPPED

6

6

RISKS AT 14 POINTS

RISKS AT 14 POINTS

14

14

CONTROLS, 3 STAGES

CONTROLS, 3 STAGES

In one common use case, AI transcription of customer calls, about half the risk points came from interactions and context rather than from any single component.

In one common use case, AI transcription of customer calls, about half the risk points came from interactions and context rather than from any single component.

MIT AI Risk Repository · NIST AI RMF · EU AI Act · ISO 42001

THE PROBLEM

THE PROBLEM

If you're accountable for AI risk, this probably sounds familiar

If you're accountable for AI risk, this probably sounds familiar

What we hear from CROs and Heads of AI Risk in the first conversation

What we hear from CROs and Heads of AI Risk in the first conversation

KNOWLEDGE

KNOWLEDGE

"My team is figuring out AI risks and controls as we go. Internal policies and standards haven't caught up."

"My team is figuring out AI risks and controls as we go. Internal policies and standards haven't caught up."

VISIBILITY

VISIBILITY

"AI models are black boxes. I can't see the data feeding them, how they behave, or what's wrapped around them in production."

"AI models are black boxes. I can't see the data feeding them, how they behave, or what's wrapped around them in production."

DEFENSIBILITY

DEFENSIBILITY

"AI standards are still evolving. I can't point to a benchmark and say 'we meet this' the way I can for SOX."

"AI standards are still evolving. I can't point to a benchmark and say 'we meet this' the way I can for SOX."

VELOCITY

VELOCITY

"I have a queue of AI use cases waiting on review, and my current assessment cycle is too long."

"I have a queue of AI use cases waiting on review, and my current assessment cycle is too long."

Governance has become the bottleneck, not the safeguard.

Governance has become the bottleneck, not the safeguard.

THE PARADIGM SHIFT

THE PARADIGM SHIFT

The risk isn't only in the tool.
It's in how the tool is used.

The risk isn't only in the tool.
It's in how the tool is used.

Most AI governance assesses the tools: the model, the vendor, the platform, each on its own. RiskAlmanac does that too. But the same model that is safe summarizing call notes is not safe when it can issue refunds or change a customer record. The tools didn't change. The usage did.

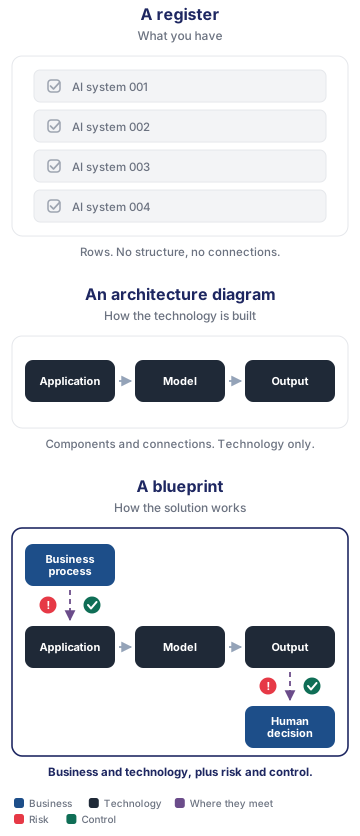
A blueprint is a business-friendly, logical description of how an AI solution works. Not a technical architecture of every physical connection, but the level you need to govern it: the process it serves, the decisions people make inside it, the data that moves through it, the models and vendors it depends on, and the points where those meet.

A blueprint is a business-friendly, logical description of how an AI solution works. Not a technical architecture of every physical connection, but the level you need to govern it: the process it serves, the decisions people make inside it, the data that moves through it, the models and vendors it depends on, and the points where those meet.

Use-case risk comes from two places a tool review cannot see: the interactions, where one tool hands off to another or to a person, and the context, meaning the process, data and permissions the solution runs in. Assessing the use takes a structured description of it. That is what a blueprint is.

Use-case risk comes from two places a tool review cannot see: the interactions, where one tool hands off to another or to a person, and the context, meaning the process, data and permissions the solution runs in. Assessing the use takes a structured description of it. That is what a blueprint is.

A register lists what you have, an architecture diagram shows how the technology is built, a blueprint shows how the solution works, business and technology together.

A blueprint is the one live view business, technology, risk and audit can all read: where risk enters, where each control attaches, and what has changed since approval.

A blueprint is the one live view business, technology, risk and audit can all read: where risk enters, where each control attaches, and what has changed since approval.

As solutions become agentic, this stops being optional. An agent can call tools, change records and act with elevated privileges across business systems, so most of what can go wrong happens in how it is used rather than in any single tool.

As solutions become agentic, this stops being optional. An agent can call tools, change records and act with elevated privileges across business systems, so most of what can go wrong happens in how it is used rather than in any single tool.

KNOWLEDGE

Curated

Curated

A curated risk and control library built on the MIT AI Risk Repository, with controls mapped to NIST AI RMF, ISO 42001 and your internal policies.

VISIBILITY

Blueprint

Blueprint

Every tool assessed, and every use captured as a blueprint: the process, decisions, data, permissions and the interactions between them. Risks and controls are derived from the blueprint, not assigned by hand.

Every tool assessed, and every use captured as a blueprint: the process, decisions, data, permissions and the interactions between them. Risks and controls are derived from the blueprint, not assigned by hand.

DEFENSIBILITY

Assured

Assured

Every control traced to the standard it came from and the point it attaches to, with evidence that it is operating as designed. RiskAlmanac also watches the running solution against the approved blueprint, so you know when it stops matching. Every approval, from the blueprint to the risks, controls and ratings, is recorded in a tamper-evident audit trail.

Every control traced to the standard it came from and the point it attaches to, with evidence that it is operating as designed. RiskAlmanac also watches the running solution against the approved blueprint, so you know when it stops matching. Every approval, from the blueprint to the risks, controls and ratings, is recorded in a tamper-evident audit trail.

VELOCITY

Automated

Automated

Intake, blueprints, risk assessment, control selection and approvals, automated at every stage. And some reviews go away entirely: a solution built on an approved blueprint pattern doesn't go back through approval, and you decide how much review each stage needs. Days, not weeks.

Intake, blueprints, risk assessment, control selection and approvals, automated at every stage. And some reviews go away entirely: a solution built on an approved blueprint pattern doesn't go back through approval, and you decide how much review each stage needs. Days, not weeks.

Assess the use, not just the tools, and you can see risk where it actually enters.

Do it from ideation, and controls go in where they belong instead of being bolted on at deployment.

"Show me where in my solution this control attaches."

"Show me where in my solution this control attaches."

Ask any vendor selling AI governance. Most will tell you what controls apply. Few will tell you where. Almost none will tell you when.

Ask any vendor selling AI governance. Most will tell you what controls apply. Few will tell you where. Almost none will tell you when.

FEWER ASSESSMENTS

FEWER ASSESSMENTS

You may have a thousand AI solutions. You don't need a thousand assessments.

You may have a thousand AI solutions. You don't need a thousand assessments.

Today every use case in the queue gets its own review, even when the fifth one is built the same way as the first.

At one large financial institution, more than 100 AI use cases fell into 4 pattern families and 8 to 10 variants. An approved pattern carries its risk assessment, its controls and their assurance, and what to monitor.

ASSESSMENT

The risks known

The risks known

The risks known

You know what can go wrong, because it was worked out when the pattern was approved.

ASSURANCE

The controls chosen

The controls chosen

The controls chosen

Which controls apply, where they attach, and the evidence that proves they work, all carried over.

Which controls apply, where they attach, and the evidence that proves they work, all carried over.

MONITORING

The monitoring defined

The monitoring defined

The monitoring defined

The signals to watch in production come with the pattern instead of being invented per solution.

The signals to watch in production come with the pattern instead of being invented per solution.

Faster assessments help. Fewer assessments scale.

New work still gets reviewed. What differs from the approved pattern goes to full review, and when a pattern changes it is re-approved and re-versioned.

HOW IT WORKS

One blueprint, traced from policy to proof

One blueprint, traced from policy to proof

The same blueprint carries the risk assessment, the controls, and the evidence. Nothing gets handed off blind.

The same blueprint carries the risk assessment, the controls, and the evidence. Nothing gets handed off blind.

Every risk and control traces back to one blueprint, sourced from policy, proven by evidence.

Every risk and control traces back to one blueprint, sourced from policy, proven by evidence.

CAPABILITIES

What lands on your desk

What lands on your desk

What risks and controls apply, where they attach, when they're needed, and how to prove them. One platform, nothing handed off between them.

What risks and controls apply, where they attach, when they're needed, and how to prove them. One platform, nothing handed off between them.

CAPABILITY 1 · WHAT

Policy Foundation

Policy Foundation

Your internal AI policies and standards mapped to a NIST AI RMF baseline, with ISO 42001 and EU AI Act alignment. Automated scope and gap analysis shows what is missing, and the missing standards get drafted rather than logged as an action item. You can start on the NIST AI RMF baseline from day one and fold your internal policies in as they land.

CAPABILITY 2 · WHERE

Solution Blueprint

Solution Blueprint

Every tool in the solution assessed, including the development tools used to build it, and every use captured as a blueprint: the process it serves, the decisions people make, the data and permissions involved, and the interactions between them. Not a register entry recording that a system exists, but a description you can design controls against. One blueprint, carried from ideation through production.

CAPABILITY 3 · WHEN

Risk and Control Tailoring

Risk and Control Tailoring

Risk assessed against the blueprint and mapped to the points where it enters. Controls drawn from NIST AI RMF, ISO 42001, and your own policies and obligations, then tailored to the solution and to the lifecycle stage it is actually in, from ideation through production. You get a stage-wise control roadmap up front, so your team can build and test controls in POC and pilot, before anything reaches production.

CAPABILITY 4 · HOW

Runtime Assurance

Runtime Assurance

For every control, RiskAlmanac defines the evidence that proves it is operating and the signals to monitor: the metrics, evaluations and telemetry to collect. Your team puts them in place, with our help if you want it, and RiskAlmanac monitors the results, along with any drift from the approved blueprint.

Defensible to your regulator. Evidenced for your auditor. In sync with what you approved.

Powered by RiskAlmanac's curated knowledge base: NIST AI RMF · ISO 42001 · EU AI Act. Risk assessment draws on external sources including MIT AI Risk Repository, CVE and ORX where they apply.

WHERE WE FIT

WHERE WE MEET

Three ways RiskAlmanac fits your stack

Three ways RiskAlmanac fits your stack

Wherever you are on AI governance, RiskAlmanac fits the way your organization runs risk and compliance today.

Wherever you are on AI governance, RiskAlmanac fits the way your organization runs risk and compliance today.

MODE 1

GRC-Connected

GRC-Connected

GRC-Connected

You already have a GRC platform. RiskAlmanac plugs into it: pulls your AI register and policies, pushes back risks, controls and compliance status per AI solution, and adds NIST AI RMF-aligned visibility your GRC doesn't have today.

You already have a GRC platform. RiskAlmanac plugs into it: pulls your AI register and policies, pushes back risks, controls and compliance status per AI solution, and adds NIST AI RMF-aligned visibility your GRC doesn't have today.

MODE 2

Observability-Paired

Observability-Paired

Observability-Paired

You already have AI observability. RiskAlmanac sits alongside it, ingesting runtime signals to flag governance drift and answer "is this solution within approved governance boundaries?" rather than "is the model behaving?"

You already have AI observability. RiskAlmanac sits alongside it, ingesting runtime signals to flag governance drift and answer "is this solution within approved governance boundaries?" rather than "is the model behaving?"

MODE 3

Standalone Platform

Standalone Platform

Standalone Platform

You're building AI governance from scratch. Full AI and technology GRC in one platform: register, blueprints, risk assessment, tailored controls and audit trail, available as SaaS for community banks, credit unions and mid-market firms.

You're building AI governance from scratch. Full AI and technology GRC in one platform: register, blueprints, risk assessment, tailored controls and audit trail, available as SaaS for community banks, credit unions and mid-market firms.

Your existing stack is welcome. We meet you where you are.

Your existing stack is welcome. We meet you where you are.

DESIGN PARTNERS

DESIGN PARTNERS

Govern your first AI solutions with us

Govern your first AI solutions with us

RiskAlmanac is taking on a small number of design partners. Together we take one or two of your priority AI solutions through all four capabilities in four weeks, and your team's feedback shapes what gets built next.

WEEK 1 · CURATE

Policy Foundation

Policy Foundation

Your policies mapped to a NIST AI RMF baseline, with ISO 42001 and EU AI Act alignment, calibrated to your organization. Gaps identified across the set, two priority standards drafted.

Your policies mapped to a NIST AI RMF baseline, with ISO 42001 and EU AI Act alignment, calibrated to your organization. Gaps identified across the set, two priority standards drafted.

WEEK 2 · BLUEPRINT

Solution Blueprint

Solution Blueprint

Your priority AI solutions captured as blueprints: the tools involved and how they're used, from process and decisions to data and permissions. The full solution, not a register row.

WEEK 3 · TAILOR

Risk and Control Tailoring

Risk and Control Tailoring

Risk assessed against each blueprint. Controls drawn from NIST AI RMF, ISO 42001 and your own policies, tailored to each solution and its lifecycle stage.

Risk assessed against each blueprint. Controls drawn from NIST AI RMF, ISO 42001 and your own policies, tailored to each solution and its lifecycle stage.

WEEK 4 · ASSURE

Runtime Assurance

Runtime Assurance

Evidence and monitoring signals defined for each control, ready for your team to put in place.

Evidence and monitoring signals defined for each control, ready for your team to put in place.

Not sure which of your AI solutions to start with? That's the first conversation.

See the demo first →

Start governing AI by design, in days, not weeks.

WHO'S BEHIND THIS

WHO'S BEHIND THIS

Thadi Murali Founder

Thadi Murali

Founder, RiskAlmanac

Founder, RiskAlmanac

Risk practitioner turned builder. I spent twenty years in financial services risk, as Managing Principal at Capco and most recently as Director of Enterprise AI and Technology Risk Governance at Freddie Mac.

As enterprises rushed to adopt AI, I saw the same gap everywhere: governance that either blocked innovation or waved it through with no real control. I built RiskAlmanac for the harder middle path.

I contribute to the NIST AI RMF Overlay Working Group, speak on AI governance including at ISACA Future Tech DC, and have a forthcoming book chapter with the University of the District of Columbia School of Business.

FRM · CISSP

FRM · CISSP

GET STARTED

Book a demo

Book a demo

A 30-minute conversation about your AI governance challenges, with a live look at the platform. RiskAlmanac is taking on a small number of design partners: see the demo first, then decide whether to govern one of your AI solutions with us.

A 30-minute conversation about your AI governance challenges, with a live look at the platform. RiskAlmanac is taking on a small number of design partners: see the demo first, then decide whether to govern one of your AI solutions with us.

NOT READY FOR A DEMO?

Send a note

Send a note

Have a question first? Tell me what you're trying to solve and I'll reply within one business day.

Have a question first? Tell me what you're trying to solve and I'll reply within one business day.

Book a demo

© 2026 RiskAlmanac. All rights reserved.

© 2026 RiskAlmanac. All rights reserved.

NIST AI RMF · EU AI Act · ISO 42001

NIST AI RMF · EU AI Act · ISO 42001